User authentication (passwords to passkeys)
Proving who a user is: from shared-computer passwords to one-time codes and phishing-resistant passkeys; the gate to every online account.
- 1961
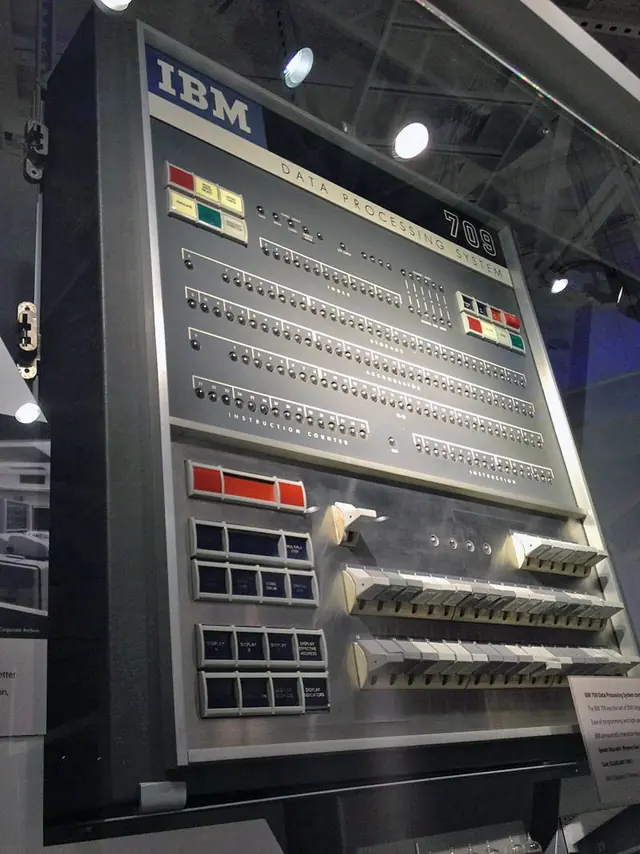
First version
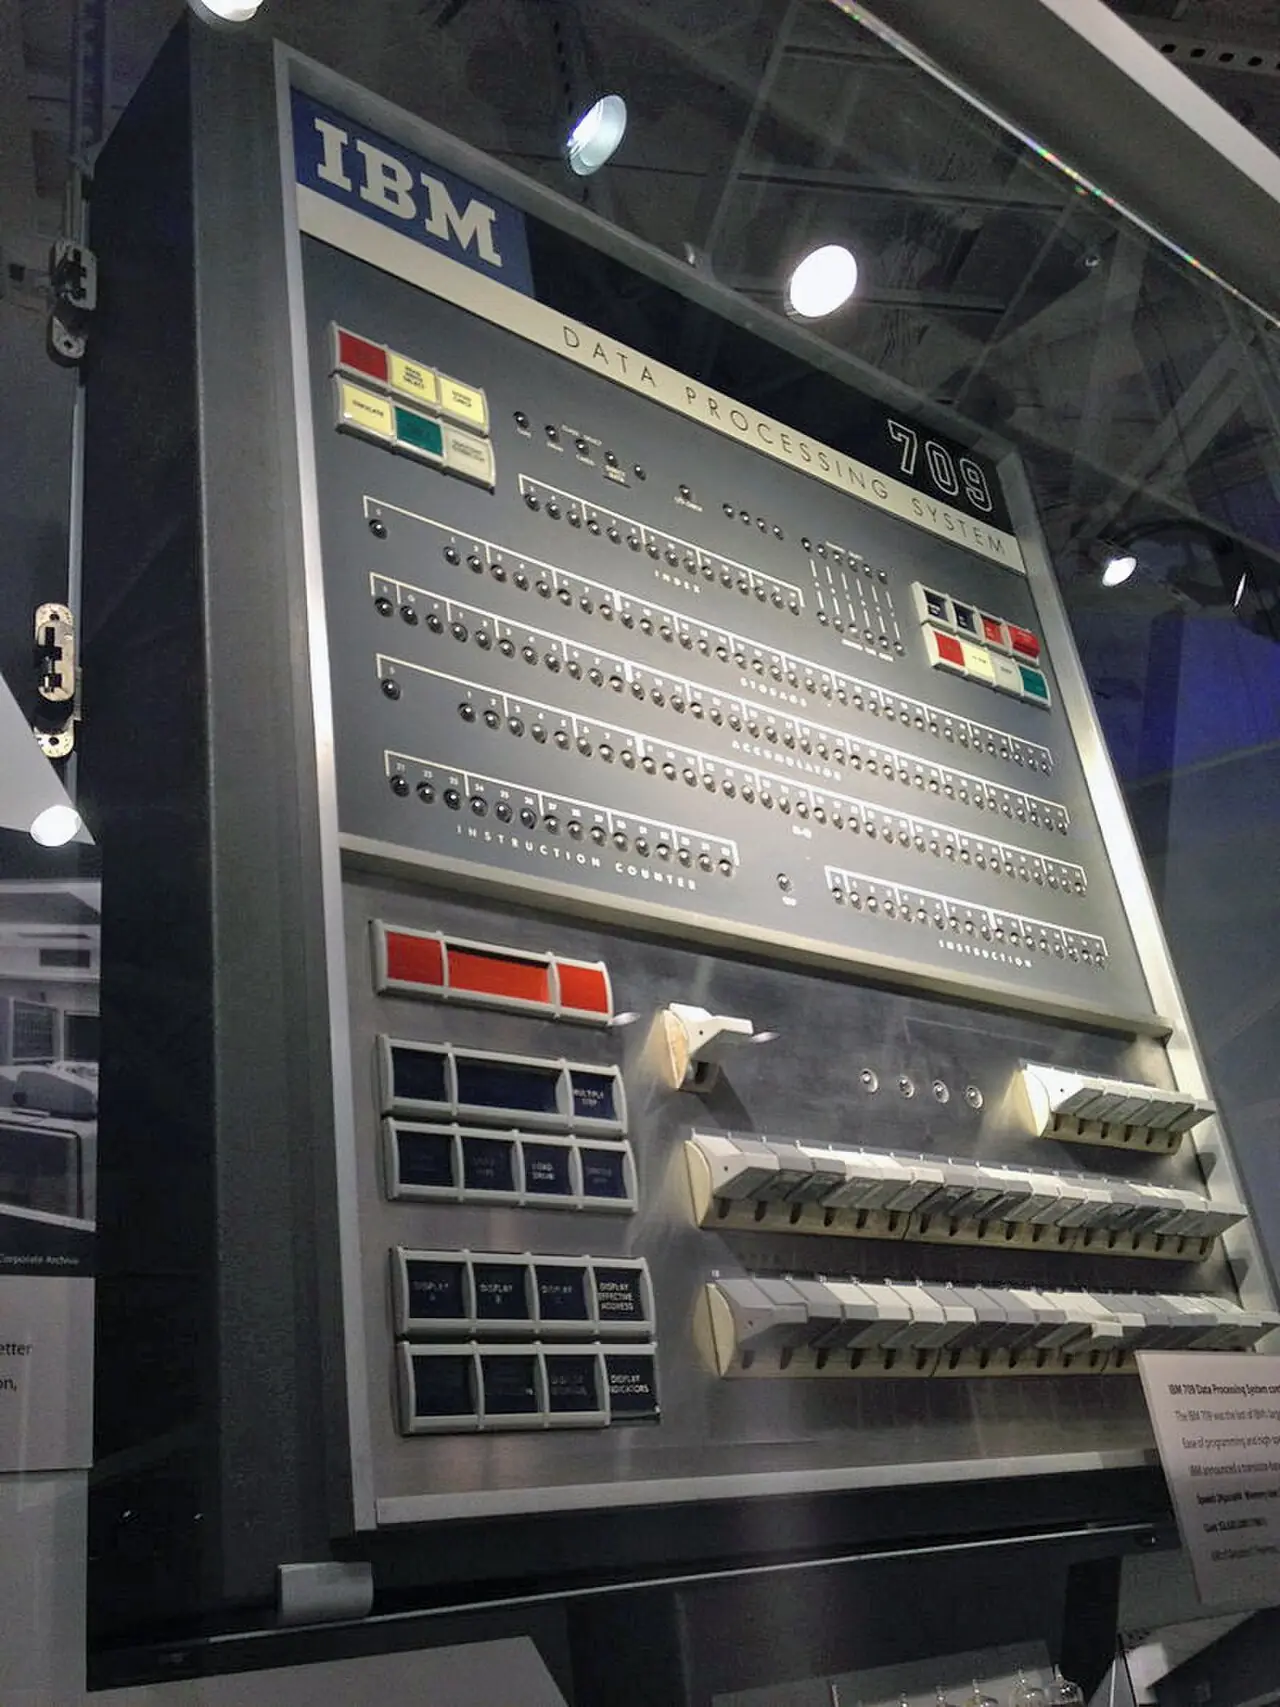
Fernando Corbato's team at MIT (CTSS computer passwords)
Image: ArnoldReinhold · CC BY-SA 3.0 · Wikimedia Commons - 1979
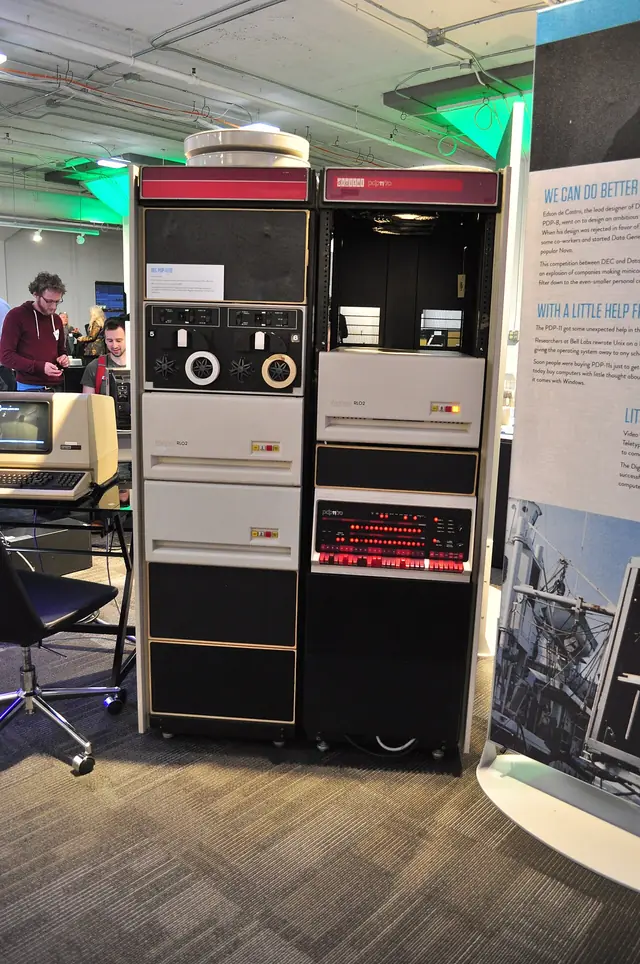
Hashed, salted passwords
Morris and Thompson's Unix design stores salted password hashes, not plaintext.
Image: Joe Mabel · CC BY-SA 3.0 · Wikimedia Commons - 1986
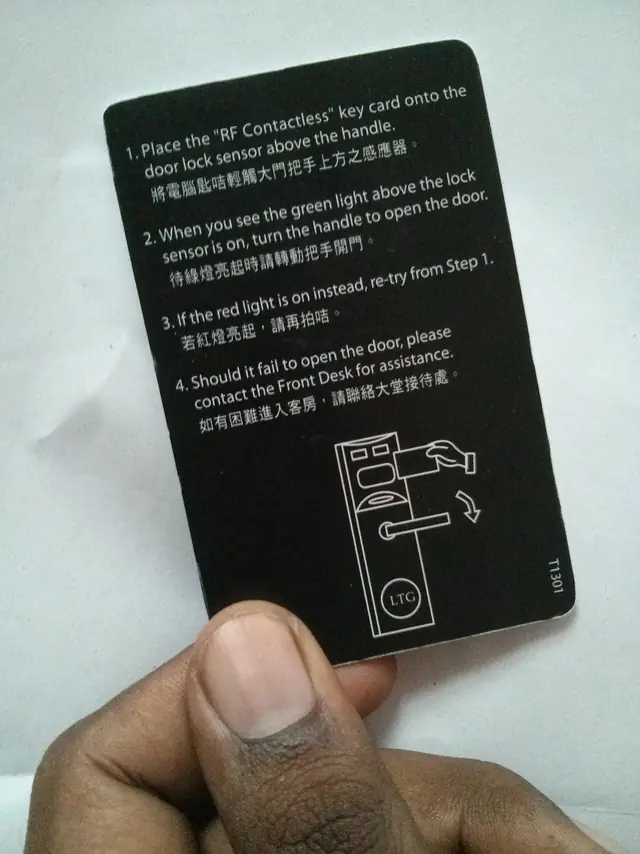
Hardware tokens (2FA)
RSA SecurID-style tokens add a one-time code as a second factor.
Image: Kavya Manohar · CC BY-SA 4.0 · Wikimedia Commons - 2011
TOTP authenticator apps
RFC 6238 time-based one-time passwords power phone authenticator apps.
Image: Google · Public domain · Wikimedia Commons - 2019
FIDO2 / WebAuthn
W3C standard for public-key, phishing-resistant login in browsers.
Image: JamesCullum · Public domain · Wikimedia Commons - 2022
Passkeys
Apple, Google and Microsoft commit to synced FIDO credentials replacing passwords.
Image: FIDO Alliance · Public domain · Wikimedia Commons